 软件开发培训班 >> 网络技术 >> 网络安全
phpcms SQL注入漏洞 adsclass.php 页面过滤不严 |
|
本文标签:phpcms,SQL注入,adsclass.php 发布日期:2010-05.24 发布作者:Jannock 影响版本:phpcms2008sp4_UTF8_100510 官方地址: www.phpcms.cn 漏洞描述: Phpcms是一款基于 PHP+Mysql 架构的网站内容管理系统,也是一个开源的 PHP 开发平台 。Phpcms 采用模块化方式开发,功能易用便于扩展,可面向大中型站点提供重量级网站建设解决方案 。3年来,凭借 Phpcms 团队长期积累的丰富的Web开发及数据库经验和勇于创新追求完美的设计理念,使得 Phpcms 得到了近10万网站的认可,并且越来越多地被应用到大中型商业网站 漏洞分析: 复制代码 代码如下:ads\include\ads.class.php function edit($ads, $adsid, $username = ) //110行 { if(!$this->check_form($ads)) return FALSE; $ads = $this->check_form($ads); if(defined(IN_ADMIN)) { $ads[fromdate] = strtotime($ads[fromdate]); $ads[todate] = strtotime($ads[todate]); } $this->adsid = $adsid; $where = adsid=.$this->adsid; if($username) $where .= " AND username=$username"; return $this->db->update($this->table, $ads, $where); } Ads\member.php if(!$c_ads->edit($info, $adsid, $_username)) showmessage($c_ads->msg(), goback); //47行 变量$adsid没有经过处理就直接进入SQL查询,造成SQL注入 。 漏洞利用: 1、注册普通会员账号 2、预订一个广告,然后修改 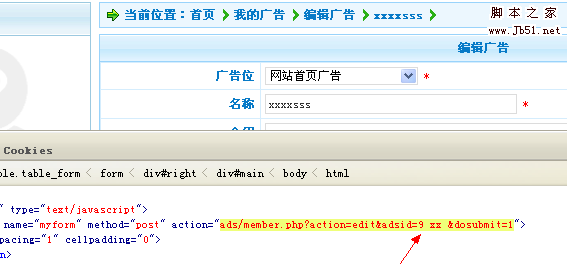 修改 adsid的值,这里是注入的地点 。提交出错信息如下:
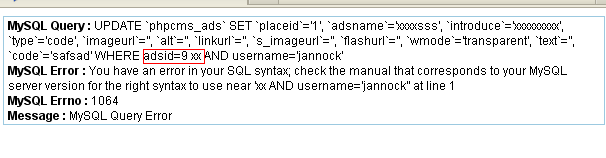 解决方案: 等官方补丁或修改 ads\include\ads.class.php $this->adsid = intval($adsid); 本文转自 黑白前线 |



